
AI and Cybersecurity: SEA Vendor Intelligence Ledger 2026 · NEW RELEASE
The Deficit of Sovereign Alignment: AI Capability vs. Southeast Asia Fit
As critical enterprise infrastructure operators accelerate multi-cloud migrations, managing data sovereignty in Southeast Asia has transitioned into a core boardroom mandate. Meeting strict regional regulations requires risk leads to establish a comprehensive framework for third-party risk management in cybersecurity that moves beyond generic software roadmaps. Logic Lock Group operates as an independent research firm, mapping how automated vendor engines manage cross-border cloud data localization rules under MAS TRM (Singapore), OJK (Indonesia), BNM RMiT (Malaysia), BOT (Thailand), Decree 356 (Vietnam), and BSP (The Philippines) perimeters to de-risk corporate technology procurement layers.
“SEA Fit” and “AI Readiness” – Master Market Quadrant
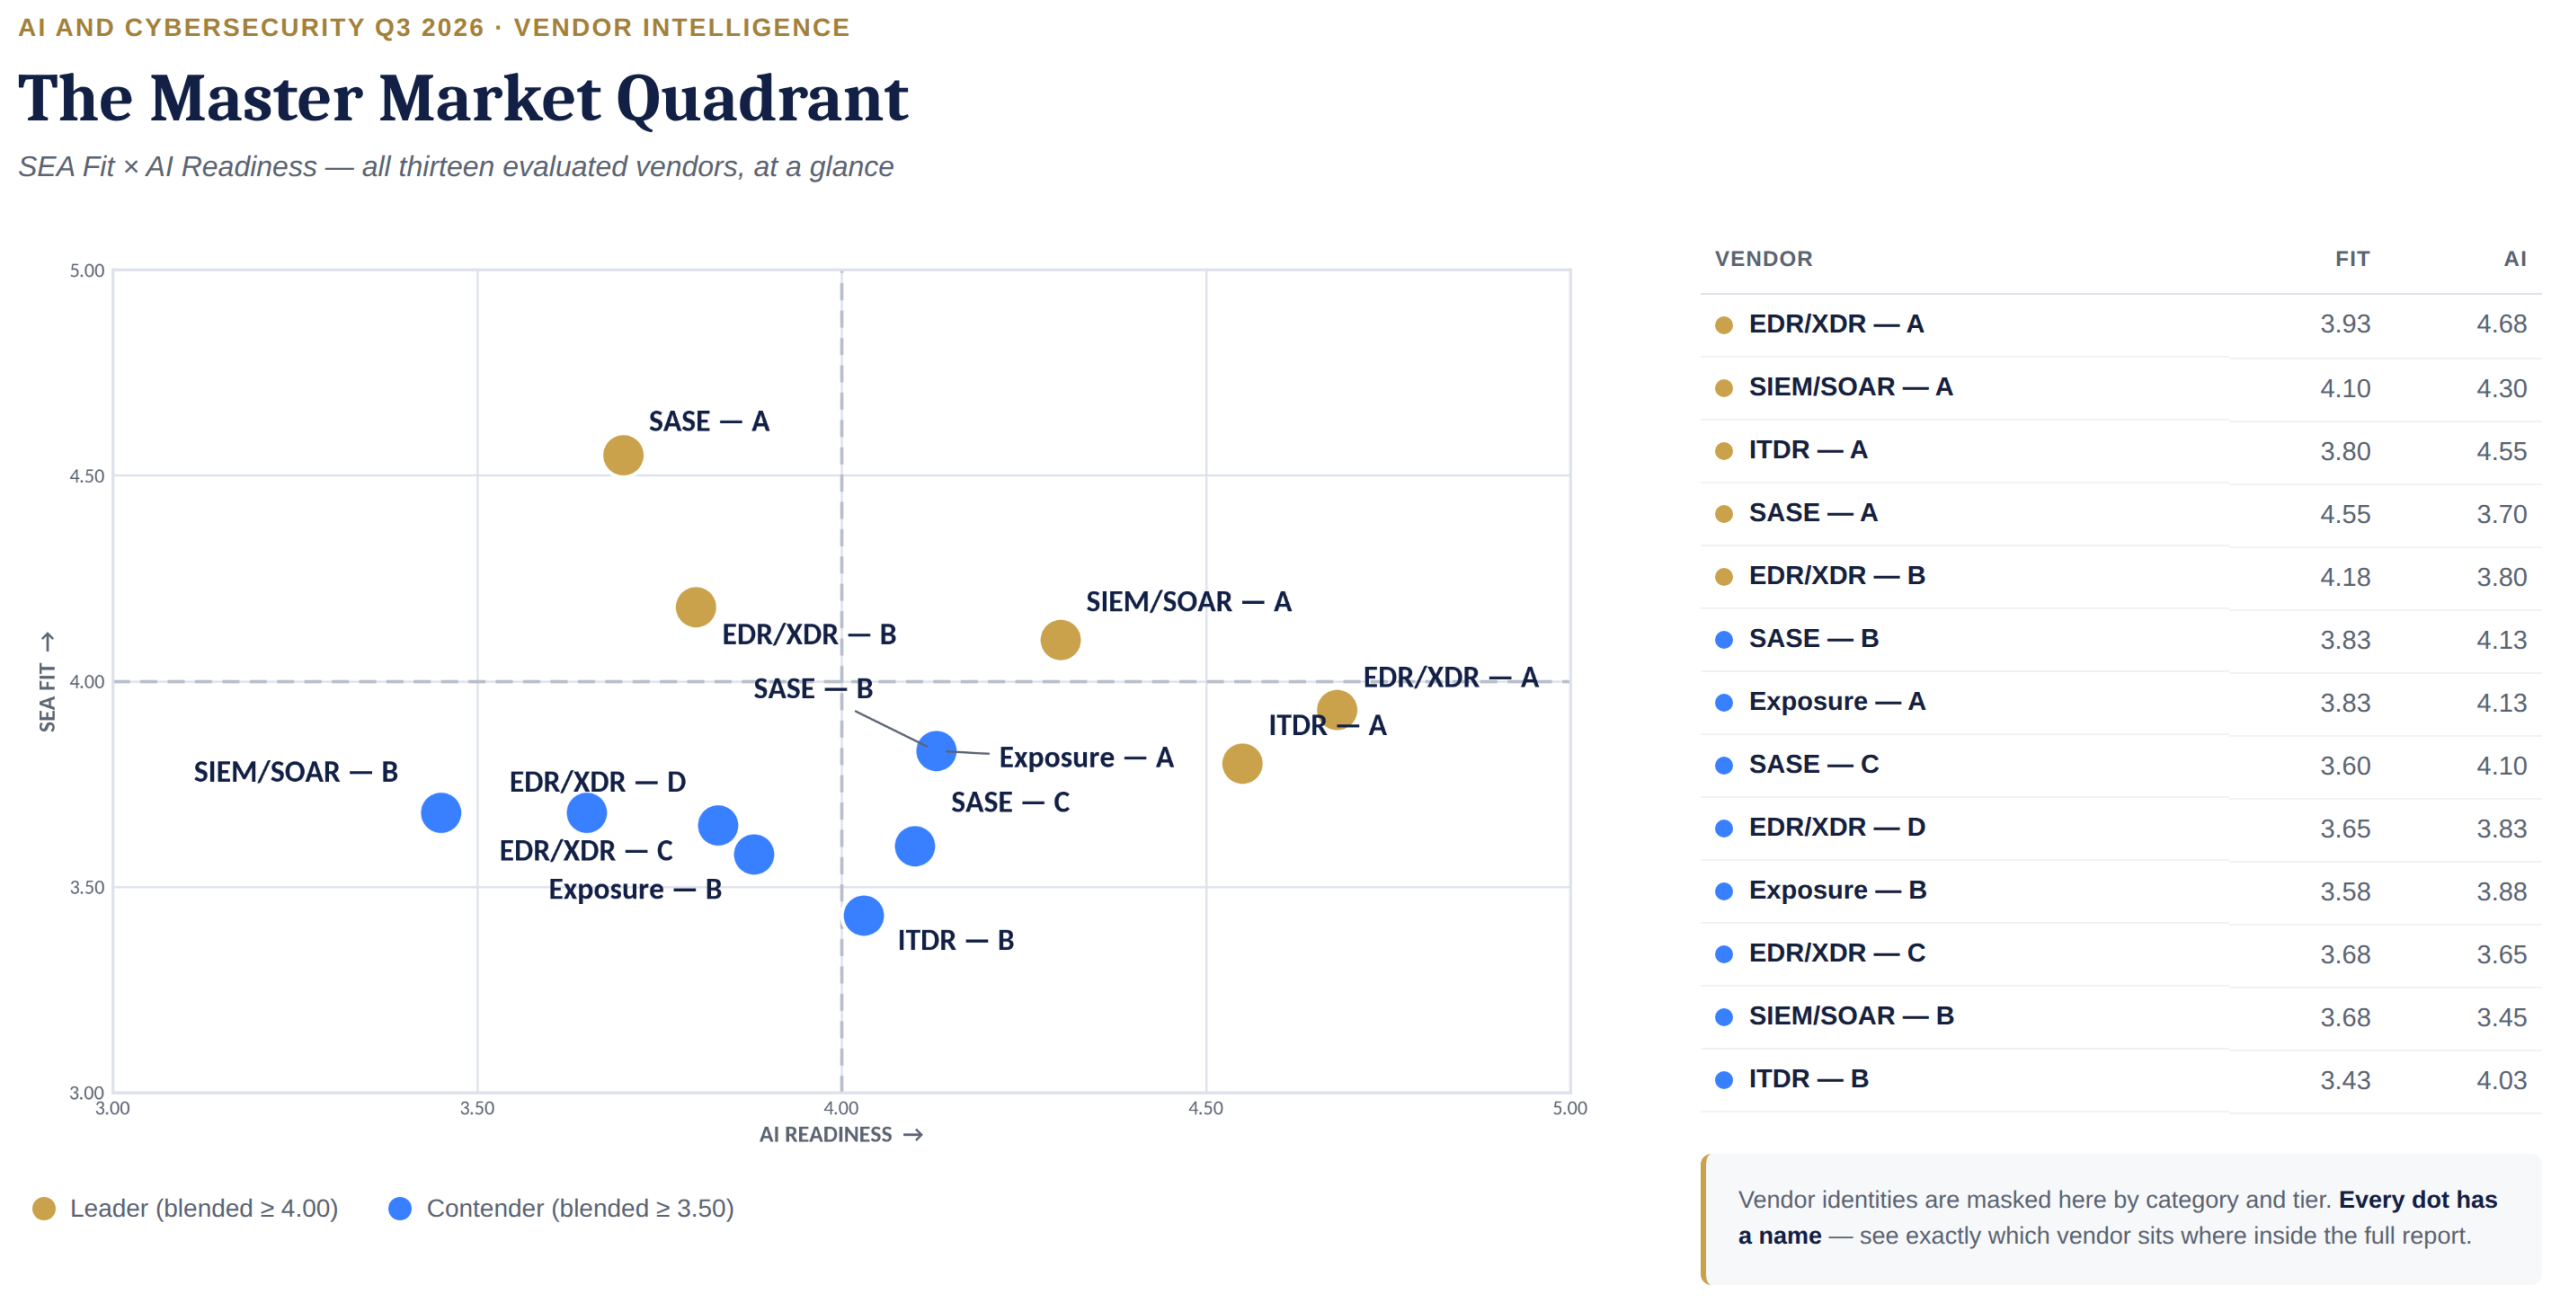
Navigating cross-border frameworks across Southeast Asia requires moving past voluntary vendor claims. Security marketing rarely distinguishes between where a platform stores data and where it actually processes it — and failing to map that identity data geography gap is exactly where compliance exposure hides. This report maps corporate security architectures against evolving regulatory mandates across six SEA markets, engineering vector by engineering vector, so your team can verify the gap directly rather than take a vendor’s word for it.
The Technical Reality: AI Readiness and Local Compliance Are Inversely Correlated
The phrase “AI-native” has become the default baseline claim across the 2026 enterprise security market. But independent architectural testing across the region reveals a consistent operational friction point for Southeast Asian infrastructure teams: the platforms with the most advanced, autonomous AI analytical engines frequently present the highest hurdles for deployment on sovereign soil. Vendors with deep localized infrastructure, in turn, rarely lead the frontier-model race.
Understanding where your current incumbent, or anything on your shortlist, actually sits against these constraints is now a baseline requirement for regional technology leadership. Do you know if your incumbent is the one? And what about everything else in your stack, or under consideration?
A Third-Party Vendor Risk Management Framework, Not Marketing Adjectives
To help senior security and technology leadership validate regional infrastructure decisions and support data-driven third-party vendor risk management programs, this research evaluates global and regional vendors against Southeast Asia specifically — and strips away the high-level promotional claims. We independently decompose every platform across three distinct, auditable engineering vectors, detailed in full in our research methodology.
1. Southeast Asia Fitness (“SEA Fit”)
- Threat Relevance: Verifying whether localized Southeast Asian attack campaigns and regional vertical variants are natively prioritized within core detection loops, not bolted on.
- Regulatory & Residency: Documenting explicit compliance posture against local data-hosting standards, sovereignty mandates, and domestic cloud access rules — from a Singapore MAS TRM compliance audit to Indonesia’s OJK data-handling requirements.
- Talent Gap: Evaluating whether the platform operates effectively under severe local administrative resource constraints without inducing critical alert fatigue.
- Delivery Layer: Assessing whether a qualified regional delivery mechanism — an in-country MSSP, named channel partner, or local support desk — actually exists to operate the platform, not just sell it.
2. The Three-Way AI Readiness Rubric
- AI-Operated Architecture: Evaluating agentic triage capabilities and automated investigation workflows built to bridge acute domestic technical talent deficits.
- AI-Analytical Engines: Evaluating the mathematical core — underlying telemetry models, behavioural baseline matrices, and anomalous log correlation logic.
- AI-Securing Safeguards: A newer governance perimeter — how the platform monitors, audits, and protects internal enterprise systems against unauthorized shadow AI tool sprawl and unmonitored autonomous model connections.
Built for Third-Party Vendor Risk Management Programs, Not Vendor Marketing
This research is fully independent — zero vendor sponsorship, zero commercial bias. It delivers rigorous technical assessments across 13 vendors that received a complete, two-axis score, spanning five heavily-contested category layers:
Beyond the 13 fully-scored vendors, this report also profiles 5 additional frontier and regional players outside the standard scoring model — 18 vendor entries in total:
2 spotlight vendors — Google (Security Operations + Mandiant + Wiz) and Sangfor Technologies. These receive argued profiles with named revisit triggers, evaluated qualitatively rather than scored on both axes.
3 regional vendors — Group-IB, Ensign InfoSecurity, and LGMS Berhad. These are scored on Southeast Asia Fitness, with qualitative AI-posture notes rather than a full AI Readiness score.
AI and Cybersecurity: SEA Vendor Intelligence Ledger 2026 · NEW RELEASE
Select Your Strategic Use of the Intelligence
Do you need to process this transaction via an official corporate purchase order (PO), bank wire transfer, or direct business invoice? We fully support standard enterprise procurement and vendor onboarding workflows.
You can select a product below and select the “Direct bank transfer” option at checkout, or email your requirements directly to [email protected] to receive an offline invoice within 1 business day.
$649 USD
Single-user license
Procurement officers and risk managers who need the core findings to clear an audit — fast.
Get the Briefing Pass$1,250 USD
Up to 10 users
CISOs and technology leaders who need board-ready materials, not just a report to read.
Get the Leadership Hub$2,450 USD
Unlimited, enterprise-wide
Enterprises, consultancies, and vendors who need the raw evidence — not just the conclusions — to build their own analysis.
Get the Strategy EngineTap a category to see everything it includes.
Free — No Purchase Required
Download a Free Sample Pack
Enter your email address and name to receive our AI and Cybersecurity: SEA Vendor Intelligence Ledger 2026 Excerpt Pack. You’ll receive one ZIP file containing three assets:
- The Report Excerpt: Real pages from the full report, including the master quadrant and one full vendor evaluation.
- The Boardroom Presentation: Sample slides from the 25-slide presentation toolkit.
- The Claims Register Spreadsheet: Real, sourced claims from the evidence base.
No email required — instant download.
Frequently Asked Questions
- How do shifting cross-border frameworks impact data sovereignty in Southeast Asia?: Achieving true operational data sovereignty in Southeast Asia requires corporate risk teams to evaluate where automated tracking layers and security telemetry are processed offshore, rather than merely checking where primary database clusters are physically hosted.
- What compliance liabilities exist within cloud data localization rules?: Navigating changing cross-border cloud data localization rules under MAS TRM, OJK, BNM RMiT, BOT, Decree 356, and BSP requires explicit engineering proof mapping automated metadata pathways to protect critical infrastructure from regulatory audit exposure.
- How does this matrix support third-party risk management in cybersecurity?: Our independent platform provides a structured framework built to optimize your third-party risk management for cybersecurity workflows. We replace voluntary vendor questionnaires with independently evaluated capability scores across 13 core global and regional infrastructure security providers.
- Can these benchmarking rows support an internal MAS TRM compliance checklist review?: While Logic Lock Group does not conduct formal certification audits, this data ledger serves as an independent technical reference. Your internal engineering and procurement teams can leverage this intelligence to streamline your institutional MAS TRM compliance checklist and multi-vendor stack reviews.